CVE-2026-111497 Explained: Node.js Brotli Decoder RCE Vulnerability (Complete Technical Analysis)

Introduction
Modern web applications process enormous volumes of compressed data every second. Whether serving APIs, delivering static assets, streaming content, or responding to browser requests, compression plays a vital role in improving performance while reducing bandwidth consumption.
One of the most efficient compression algorithms available today is Brotli, developed by Google and widely adopted across modern web servers, browsers, and application frameworks. Node.js includes native Brotli support through its compression APIs, allowing developers to efficiently compress and decompress data without relying on third-party libraries.
Because Brotli is deeply integrated into Node.js, any vulnerability affecting its implementation has the potential to impact countless applications running across cloud platforms, enterprise environments, SaaS products, and public-facing web services.
On October 21, 2026, the Node.js Security Team released emergency security updates addressing ten vulnerabilities across the supported release lines. Among them, one vulnerability immediately attracted the attention of the security community:
CVE-2026-111497 — Node.js Brotli decoder out-of-bounds write permits Remote Code Execution (RCE).
Unlike many application-specific vulnerabilities, this flaw exists within the Node.js runtime itself. As a result, developers cannot simply update their application code or dependencies to resolve the issue. The underlying Node.js installation must be upgraded to a patched release.
Although exploitation depends on application-specific conditions, the possibility of memory corruption leading to arbitrary code execution makes CVE-2026-111497 one of the most significant Node.js vulnerabilities disclosed in recent years.
This article explains how the vulnerability works, why it matters, which environments are affected, and what organizations should do to reduce their risk.
Executive Summary
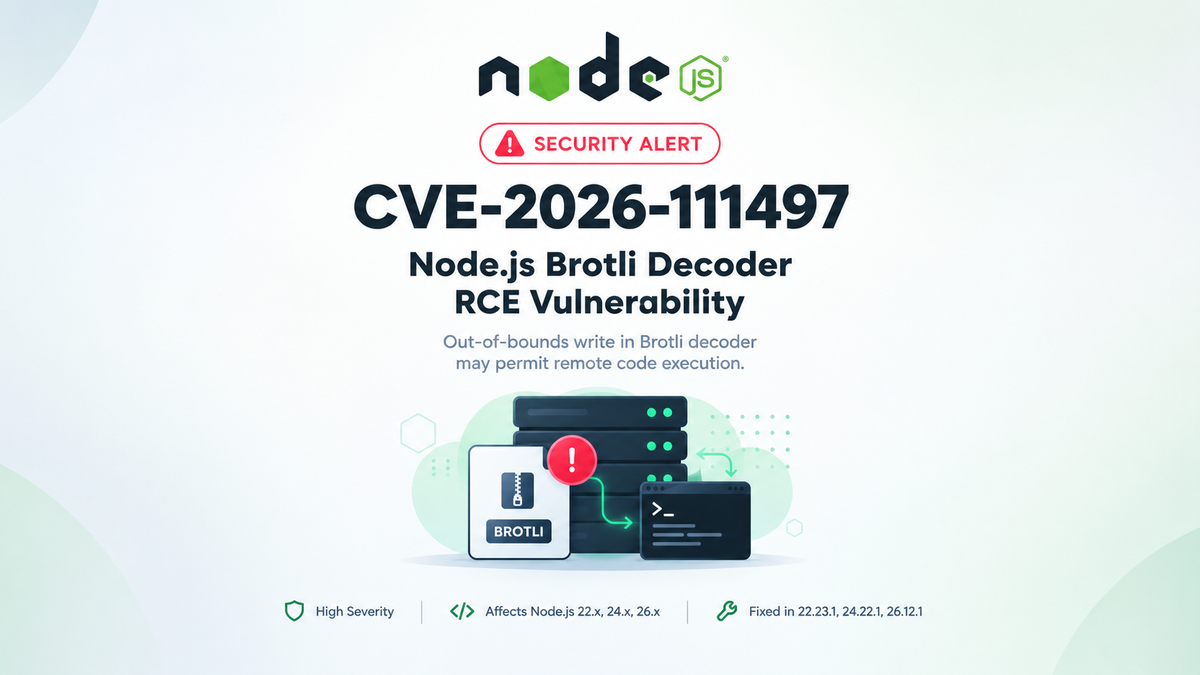
CVE-2026-111497 is a High Severity vulnerability affecting the Brotli decoder implementation included with Node.js.
According to the official Node.js Security Release, the vulnerability is an out-of-bounds write that may permit Remote Code Execution (RCE) under vulnerable conditions.
The issue affects all supported Node.js release lines at the time of disclosure:
- Node.js 22.x
- Node.js 24.x
- Node.js 26.x
The vulnerability was addressed through the October 21, 2026 security releases with patched versions:
- Node.js v22.23.1
- Node.js v24.22.1
- Node.js v26.12.1
Organizations operating internet-facing Node.js services should prioritize updating to one of these releases as soon as possible. Because the vulnerability exists within the runtime rather than application code, updating frameworks such as Express.js or NestJS alone does not provide protection.
Understanding Brotli in Node.js
Before examining the vulnerability itself, it is important to understand why Brotli exists and why vulnerabilities affecting it can have such a broad impact.
Brotli is a modern compression algorithm designed to provide better compression ratios than Gzip while maintaining efficient decompression performance. Today it is supported by all major web browsers and is commonly used to compress HTML, JavaScript, CSS, JSON, API responses, and other web content.
Node.js exposes native Brotli functionality through its built-in compression APIs, allowing applications to both compress and decompress data without requiring external libraries.
This functionality is frequently used by:
- Reverse proxies
- REST APIs
- GraphQL services
- Content Delivery Networks
- Server-side rendering frameworks
- Asset optimization pipelines
- Microservices
- Edge computing platforms
Because Brotli processing often occurs automatically, many developers may not even realize their applications rely on it.
Whenever compressed data is received from clients, upstream services, or other infrastructure components, the Brotli decoder becomes responsible for interpreting that compressed stream.
If flaws exist during that decoding process, specially crafted compressed input may trigger unexpected behavior inside the runtime itself.
That is precisely the scenario addressed by CVE-2026-111497.
Technical Analysis
The official Node.js advisory describes CVE-2026-111497 as:
Node.js Brotli decoder out-of-bounds write permits remote code execution.
Although the advisory intentionally avoids publishing exploit details before organizations have had an opportunity to patch their systems, the vulnerability classification provides several important insights.
Unlike an out-of-bounds read, which generally exposes existing memory contents, an out-of-bounds write allows data to be written beyond the boundaries of an allocated memory region.
Memory corruption vulnerabilities of this nature are particularly dangerous because they may allow attackers to overwrite adjacent memory structures that influence program execution.
Depending on the surrounding memory layout, successful exploitation may lead to:
- Process crashes
- Denial of Service (DoS)
- Corruption of application state
- Arbitrary memory modification
- Remote Code Execution
The Node.js Security Team specifically notes that this vulnerability permits Remote Code Execution, indicating that researchers demonstrated a practical path from memory corruption to arbitrary code execution under vulnerable conditions.
While Node.js applications are generally written in JavaScript, the runtime itself contains large portions of native C and C++ code. Brotli decoding occurs within these lower-level native components where traditional memory safety protections provided by JavaScript no longer apply.
This distinction is important.
JavaScript developers often assume memory corruption is impossible because the language itself is memory-safe. However, vulnerabilities within native runtime components bypass those protections entirely because they execute below the JavaScript engine.
Consequently, vulnerabilities affecting Node.js internals have the potential to compromise every JavaScript application running on the affected runtime.
Why Out-of-Bounds Writes Are So Dangerous
Modern operating systems implement numerous security mechanisms intended to make memory corruption more difficult to exploit.
These include:
- Address Space Layout Randomization (ASLR)
- Data Execution Prevention (DEP)
- Stack canaries
- Control Flow Integrity (CFI)
- Read-only memory protections
These mitigations significantly increase exploitation complexity.
However, they do not eliminate memory corruption vulnerabilities.
Out-of-bounds writes remain among the most severe classes of software vulnerabilities because they permit attackers to modify memory that should never be accessible.
If an attacker can influence what data is written and where it is written, carefully crafted payloads may redirect execution flow toward malicious code.
For this reason, out-of-bounds write vulnerabilities are frequently classified as potential Remote Code Execution issues until proven otherwise.
The Node.js advisory reflects exactly that assessment by classifying CVE-2026-111497 as a High severity vulnerability capable of permitting RCE.
Why This Vulnerability Matters
At first glance, the vulnerability may appear to affect only applications that explicitly use Brotli compression.
In reality, the exposure is much broader.
Many popular frameworks automatically negotiate Brotli compression with browsers and upstream services.
Cloud platforms frequently enable Brotli by default.
Content delivery networks routinely compress assets using Brotli.
Reverse proxies often exchange Brotli-compressed responses with backend applications.
Developers may therefore inherit vulnerable behavior without ever writing Brotli-specific code themselves.
Because the vulnerability exists inside the Node.js runtime, every application sharing that runtime potentially inherits the same weakness.
This dramatically increases the overall attack surface compared to a vulnerability confined to a single framework or package.
For organizations operating large Node.js deployments, updating every affected runtime should therefore become a priority immediately following disclosure.
Exploitation Scenario
The Node.js Security Team has intentionally withheld detailed exploitation information to provide organizations with time to deploy the available security updates. This responsible disclosure approach is common practice for vulnerabilities with significant security implications, particularly those that may lead to Remote Code Execution.
While no public proof-of-concept (PoC) exploit was available at the time of writing, understanding a realistic attack scenario helps explain why security teams should prioritize remediation.
A typical attack chain could begin with an attacker identifying an internet-facing Node.js application that accepts compressed input or processes Brotli-compressed content as part of its normal operation. Rather than targeting vulnerabilities in the application itself, the attacker would focus on triggering the vulnerable code path inside Node.js' native Brotli decoder.
By supplying a specially crafted Brotli-compressed payload, the attacker may trigger the out-of-bounds write condition described in the official advisory. If the corrupted memory can be manipulated in a predictable manner, it may become possible to alter the execution flow of the process.
Successful exploitation could ultimately allow arbitrary code execution within the privileges of the Node.js process.
Although exploitation of modern memory corruption vulnerabilities is rarely straightforward, history has shown that determined attackers frequently develop reliable techniques once technical details become public.
Organizations should therefore avoid assuming that the absence of a public exploit equates to safety. Once patches are released, reverse engineering those patches to understand the underlying vulnerability is a common technique used by both security researchers and threat actors.
Why Remote Code Execution Is a Serious Threat
Among software vulnerabilities, Remote Code Execution represents one of the highest-impact outcomes.
Unlike vulnerabilities that merely expose information or temporarily disrupt service availability, Remote Code Execution allows attackers to execute commands directly on the affected server.
The practical consequences depend largely on how the Node.js application is deployed and what permissions the process possesses.
In many production environments, successful exploitation could allow attackers to:
- Execute arbitrary operating system commands.
- Install persistent backdoors or web shells.
- Read sensitive application files.
- Access environment variables containing API keys or secrets.
- Interact with connected databases.
- Deploy ransomware or cryptomining malware.
- Move laterally into internal infrastructure.
Even if the compromised application runs with limited privileges, attackers often use the initial foothold to identify additional weaknesses that enable privilege escalation or further compromise.
For organizations hosting customer-facing services, a single vulnerable Node.js instance may become the entry point into a much larger environment.
Who Is Affected?
According to the official Node.js security release, CVE-2026-111497 affects all supported release lines available prior to the October 21, 2026 security updates.
Affected release lines include:
- Node.js 22.x
- Node.js 24.x
- Node.js 26.x
The vulnerability has been addressed in the following patched releases:
| Release Line | Patched Version |
|---|---|
| Node.js 22.x | 22.23.1 |
| Node.js 24.x | 24.22.1 |
| Node.js 26.x | 26.12.1 |
Administrators should verify both the installed Node.js version and the runtime actually executing production workloads. In containerized or orchestrated environments, outdated images may continue to run vulnerable versions even after newer packages become available.
It is equally important to remember that updating application dependencies does not resolve this issue. Since the vulnerability exists within the Node.js runtime itself, only upgrading to a patched Node.js release provides protection.
Commonly Affected Environments
Because Node.js powers a wide range of modern applications, the potential exposure extends across multiple industries.
Examples of environments that may be affected include:
- Express.js applications
- NestJS services
- Next.js deployments
- Nuxt.js server-side rendering environments
- Fastify APIs
- Koa applications
- Strapi and Keystone CMS deployments
- Headless CMS platforms
- Serverless functions using vulnerable Node.js runtimes
- Docker containers running affected Node.js images
- Internal APIs and microservices
Applications hosted on cloud platforms are not automatically protected simply because the underlying infrastructure is managed. Organizations remain responsible for ensuring their applications run on supported Node.js versions.
If custom Docker images or long-lived virtual machines are used, administrators should verify that updated runtime packages have actually been deployed.
Business Impact
Although the vulnerability affects software at a technical level, the consequences extend far beyond system administrators.
A successful compromise may interrupt business operations, expose customer information, damage organizational reputation, and result in regulatory obligations depending on the nature of the affected data.
For organizations providing Software-as-a-Service (SaaS) platforms, exploitation could affect multiple customers simultaneously.
Financial institutions may face increased operational risk due to service disruptions.
Healthcare providers could experience exposure of sensitive patient information.
Government organizations may face unauthorized access to public-facing services.
E-commerce platforms risk theft of customer information, payment-related data, or disruption of critical online services.
Because Node.js is frequently deployed as part of larger microservice architectures, compromising one service may also provide attackers with opportunities to access internal APIs, authentication services, or backend infrastructure.
Detecting Potential Exposure
Unlike vulnerabilities that generate obvious error messages, memory corruption issues often leave very little evidence during the initial stages of exploitation.
Security teams should therefore adopt a proactive approach when assessing their environment.
Begin by inventorying every Node.js installation across production, staging, and development environments.
Administrators should verify:
- Installed Node.js versions.
- Running Node.js processes.
- Container base images.
- CI/CD build environments.
- Serverless runtime versions.
- Platform-as-a-Service runtime configurations.
After patching, monitoring should continue for signs of suspicious behavior, including unexpected process crashes, repeated application restarts, abnormal memory consumption, or unexplained outbound network connections.
Although these indicators are not unique to CVE-2026-111497, they may help identify attempted exploitation or post-compromise activity.
Mitigation and Remediation
The most effective mitigation is straightforward: upgrade to a patched version of Node.js provided by the Node.js Security Team.
Organizations should install:
- Node.js 22.23.1
- Node.js 24.22.1
- Node.js 26.12.1
or any newer release that includes the security fix.
After updating the runtime, all Node.js services should be restarted to ensure the patched binaries are loaded into memory.
For environments using Docker or Kubernetes, rebuilding application images is equally important. Updating the package on a build server does not automatically update containers already running in production.
Organizations should also review deployment pipelines to ensure future builds inherit the patched runtime rather than referencing older base images.
Where immediate patching is not possible, organizations should reduce their exposure by limiting unnecessary internet access, placing vulnerable services behind reverse proxies or Web Application Firewalls (WAFs), enforcing least-privilege execution, and closely monitoring application logs for unusual behavior.
These measures should be viewed only as temporary risk-reduction strategies rather than permanent solutions.
Ultimately, upgrading to a patched Node.js release remains the only reliable method of eliminating the vulnerability.
Lessons Learned
CVE-2026-111497 is another reminder that vulnerabilities affecting foundational software components can have consequences far beyond a single application or framework.
Unlike a vulnerability in an individual npm package, this issue resides within the Node.js runtime itself. That distinction significantly expands its potential impact because every application running on a vulnerable Node.js installation inherits the same underlying weakness.
The disclosure also reinforces several important security principles.
First, organizations should treat runtime updates with the same urgency as operating system or browser security patches. While many development teams routinely update npm dependencies, upgrades to the underlying runtime are often delayed due to compatibility concerns or operational overhead.
Second, software inventories remain critical. Security teams cannot remediate vulnerabilities they cannot identify. Maintaining visibility into Node.js versions across production servers, containers, CI/CD pipelines, and serverless environments enables faster incident response when vulnerabilities are disclosed.
Finally, the security release highlights why defense-in-depth remains essential. Even when vulnerabilities cannot be prevented entirely, layered security controls—including network segmentation, runtime monitoring, least-privilege execution, endpoint detection, and Web Application Firewalls (WAFs)—can significantly reduce the impact of successful exploitation.
Timeline of Disclosure
The Node.js Security Team announced the Wednesday, October 21, 2026 Security Releases, addressing a total of ten vulnerabilities across the supported Node.js release lines. Among the disclosed issues, four were rated High Severity, with CVE-2026-111497 receiving significant attention due to its potential to permit Remote Code Execution through an out-of-bounds write in the Brotli decoder. :chatgpt-content-reference{index="0"}
The coordinated security release included updated versions for the supported release lines:
| Release Line | Fixed Version |
|---|---|
| Node.js 22.x | 22.23.1 |
| Node.js 24.x | 24.22.1 |
| Node.js 26.x | 26.12.1 |
The Node.js project intentionally withheld detailed exploitation information during the initial disclosure to encourage rapid patch adoption before technical analysis or proof-of-concept exploits become publicly available. This follows established responsible disclosure practices commonly used for high-impact vulnerabilities. :chatgpt-content-reference{index="1"}
Security Recommendations
Organizations using Node.js in production should treat this vulnerability as a high-priority security update.
Security teams should begin by identifying every Node.js runtime deployed across production, staging, development, and CI/CD environments. Special attention should be given to container images and long-lived virtual machines, as these frequently continue running outdated runtimes even after patched versions have been released.
After upgrading to a fixed version, administrators should restart all Node.js processes to ensure the updated runtime is loaded into memory. In Kubernetes or containerized environments, this includes rebuilding container images and redeploying workloads rather than simply updating packages on the host system.
Although no public indicators of compromise specific to CVE-2026-111497 have been published at the time of writing, organizations should continue monitoring for abnormal application crashes, unexpected process behavior, unexplained outbound connections, or unauthorized file modifications that may indicate attempted exploitation or post-compromise activity.
Maintaining a structured vulnerability management process—including routine software inventories, timely patch deployment, continuous monitoring, and periodic security assessments—remains one of the most effective ways to reduce exposure to newly disclosed vulnerabilities.
Final Thoughts
The disclosure of CVE-2026-111497 demonstrates that even mature, widely trusted technologies can contain critical vulnerabilities with far-reaching implications.
Although most developers interact with Node.js through JavaScript, the runtime itself depends on complex native components written in C and C++. Vulnerabilities within these lower-level components can bypass many of the safety guarantees that developers typically associate with JavaScript, making runtime security updates just as important as application-level patches.
While the Node.js Security Team acted quickly by releasing coordinated updates across all supported release lines, the responsibility for remediation ultimately rests with organizations operating vulnerable systems.
Promptly upgrading to a patched Node.js release, validating deployment pipelines, rebuilding affected containers, and maintaining ongoing visibility into runtime versions will significantly reduce the risk posed by this and future runtime vulnerabilities.
As attackers increasingly reverse engineer security patches shortly after release, organizations that respond quickly to vendor advisories consistently place themselves in a stronger position than those that delay critical updates.
References
-
Node.js Project — Wednesday, October 21, 2026 Security Releases
https://nodejs.org/en/blog/vulnerability/october-2026-security-releases -
CVE Record — CVE-2026-111497
https://www.cve.org/CVERecord?id=CVE-2026-111497 -
National Vulnerability Database (NVD) — CVE-2026-111497 (when fully published)
https://nvd.nist.gov/ -
Node.js Security Policy
https://nodejs.org/en/security/ -
Vercel Security Bulletin — Node.js Security Advisory
https://vercel.com/kb/bulletin/node-js-security-advisory