Full root access
Log in as root (or Administrator) and configure the server exactly the way your project needs.
Shared hosting: No root or sudo access
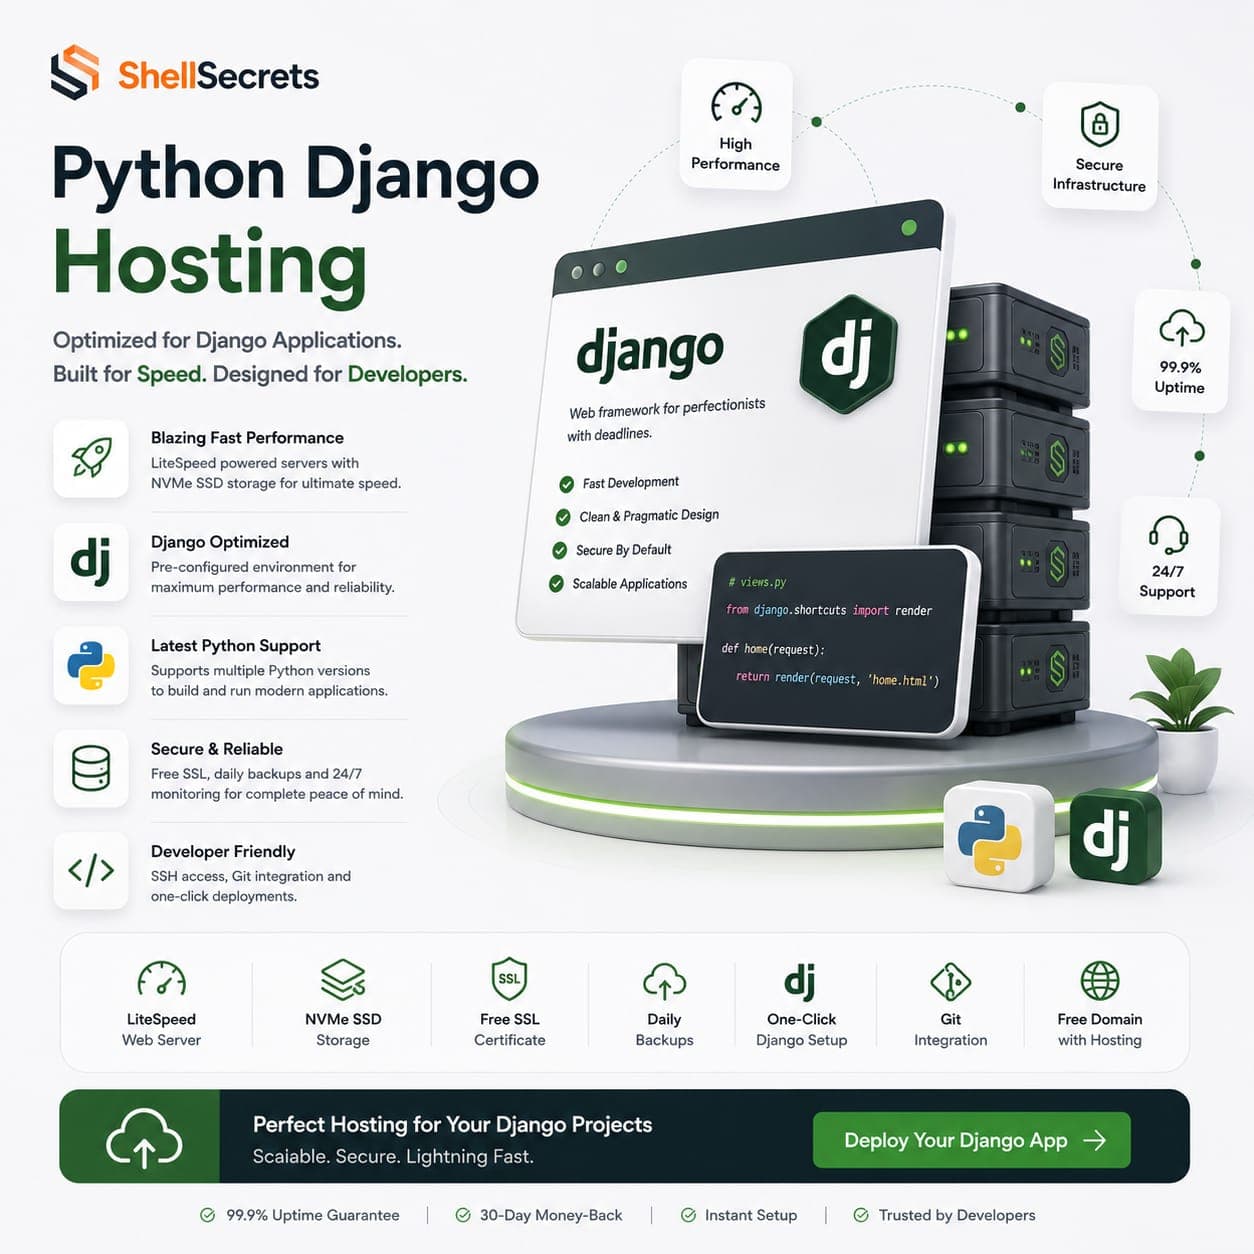
Deploy Python apps, Django projects, Flask services, FastAPI endpoints, scripts, and workers on secure VPS servers with SSL, databases, backups, and expert support.
Django, Flask, FastAPI ready
Python runtime support
Free SSL certificates
Database-ready hosting
Automatic backups
24/7 developer support
From $5.83/mo
No hidden fees
Always-on infrastructure built for scale.
Talk to Our Experts
Get tailored guidance for your goals.
Deploy Python applications, APIs, background workers, and Django projects with SSL, backups, databases, SSH, and practical support.
Plan Duration
vCPU
1
RAM
1 GB
Storage
20 GB SSD
IPv4
Bandwidth
3 TB
$5.83/mo
$70/year
1 vCPU, 1 GB RAM, 20 GB SSD, 3 TB bandwidth — US datacenter.
$5.83/mo
For 12 months, you pay $70.
vCPU: 1
RAM: 1 GB
Storage: 20 GB SSD
Bandwidth: 3 TB
IP: 1 IPv4 address
vCPU
2
RAM
2 GB
Storage
35 GB SSD
IPv4
Bandwidth
5 TB
$9.17/mo
$110/year
2 vCPU, 2 GB RAM, 35 GB SSD, 5 TB bandwidth — US datacenter.
$9.17/mo
For 12 months, you pay $110.
vCPU: 2
RAM: 2 GB
Storage: 35 GB SSD
Bandwidth: 5 TB
IP: 1 IPv4 address
vCPU
3
RAM
4 GB
Storage
60 GB SSD
IPv4
Bandwidth
7 TB
$15.83/mo
$190/year
3 vCPU, 4 GB RAM, 60 GB SSD, 7 TB bandwidth — US datacenter.
$15.83/mo
For 12 months, you pay $190.
vCPU: 3
RAM: 4 GB
Storage: 60 GB SSD
Bandwidth: 7 TB
IP: 1 IPv4 address
Backups: every 4 weeks
Ubuntu, Debian, AlmaLinux and more
Full root access
No setup fee
vCPU
6
RAM
6 GB
Storage
100 GB SSD
IPv4
Bandwidth
12 TB
$31.83/mo
$382/year
6 vCPU, 6 GB RAM, 100 GB SSD, 12 TB bandwidth — US datacenter.
$31.83/mo
For 12 months, you pay $382.
vCPU: 6
RAM: 6 GB
Storage: 100 GB SSD
Bandwidth: 12 TB
IP: 1 IPv4 address
Backups: every 4 weeks
Ubuntu, Debian, AlmaLinux and more
Full root access
No setup fee
vCPU
7
RAM
8 GB
Storage
150 GB SSD
IPv4
Bandwidth
20 TB
$38.33/mo
$460/year
7 vCPU, 8 GB RAM, 150 GB SSD, 20 TB bandwidth — US datacenter.
$38.33/mo
For 12 months, you pay $460.
vCPU: 7
RAM: 8 GB
Storage: 150 GB SSD
Bandwidth: 20 TB
IP: 1 IPv4 address
Backups: every 4 weeks
Ubuntu, Debian, AlmaLinux and more
Full root access
No setup fee
Choose your Python version, run Gunicorn or Uvicorn behind your own web server, and keep Celery workers running, without shared-hosting process or I/O caps.
Log in as root (or Administrator) and configure the server exactly the way your project needs.
Shared hosting: No root or sudo access
Run as many processes and concurrent connections as your server's resources allow — no per-account NPROC or entry-process caps.
Shared hosting: Per-account process caps
No LVE-style per-account CPU or I/O limits. Your workload uses the vCPU and disk throughput your plan provides.
Shared hosting: CPU and I/O limited per account
Resources allocated to your server rather than pooled with every other account on a shared host.
Shared hosting: Resources shared between accounts
Any runtime, language version, database, container engine, custom software, or system package you need.
Shared hosting: Limited to the host's software
Set your own firewall rules, open the ports you need, and apply your own SSH and hardening policies.
Shared hosting: Host-wide rules you can't change
Keep queue workers, WebSockets, and long-running services up, and schedule cron jobs without restriction.
Shared hosting: Long-running processes restricted
Pick the Linux distribution you prefer and reinstall a clean image whenever you want a fresh start.
Shared hosting: OS fixed by the host
Move code, dependencies, env vars, databases, SSL, and DNS with a planned deployment path.
Python migrations need runtime checks, package validation, database testing, static file review, environment handling, and post-deploy log checks. We help move the app with fewer surprises.
Connect with our DevOps experts for fast, reliable support.
Python hosting works best when runtime, dependencies, framework settings, database access, and logs are handled as one workflow.
Select a Python runtime, isolate dependencies, and prepare application settings cleanly.
Deploy Django, Flask, FastAPI, WSGI, ASGI, APIs, scripts, and worker-based projects.
Connect the app to MySQL, PostgreSQL, Redis, or external managed databases as needed.
Review SSL, DNS, logs, backups, cron jobs, and production behavior after launch.
Most deployment issues come from dependency conflicts, missing environment variables, database settings, static files, SSL, or DNS. We surface those checks before traffic reaches the app.
Use familiar Python frameworks while hosting keeps SSL, DNS, backups, email, databases, and support in one managed place.
Deploy Django projects, APIs, scripts, and worker services while keeping runtime, dependencies, databases, and logs visible.
Deploy Django projects with SSL, DNS, database access, static file planning, backups, and migration support.
Run Flask and FastAPI services with clean runtime setup, database connections, and production checks.
Use root SSH access, dependency setup, logs, and support for deploy-time issues.
Get practical help with migrations, Python versions, dependency errors, environment variables, static files, SSL, DNS, database connections, and runtime logs.
Get round-the-clock guidance from experienced support engineers.
Open a ticket for technical issues, migrations, billing, or service help.
Talk with our team when you need quick help with urgent questions.
Browse knowledge base articles, setup guides, and troubleshooting notes.
Answers about managed Python hosting, Django, Flask, FastAPI, databases, SSH, migration, and deployment support.
Python Django hosting is managed hosting for Python applications, Django projects, Flask apps, FastAPI services, APIs, scripts, and background workers.
Explore practical hosting, server, cloud, and DevOps guides from the ShellSecrets articles hub.
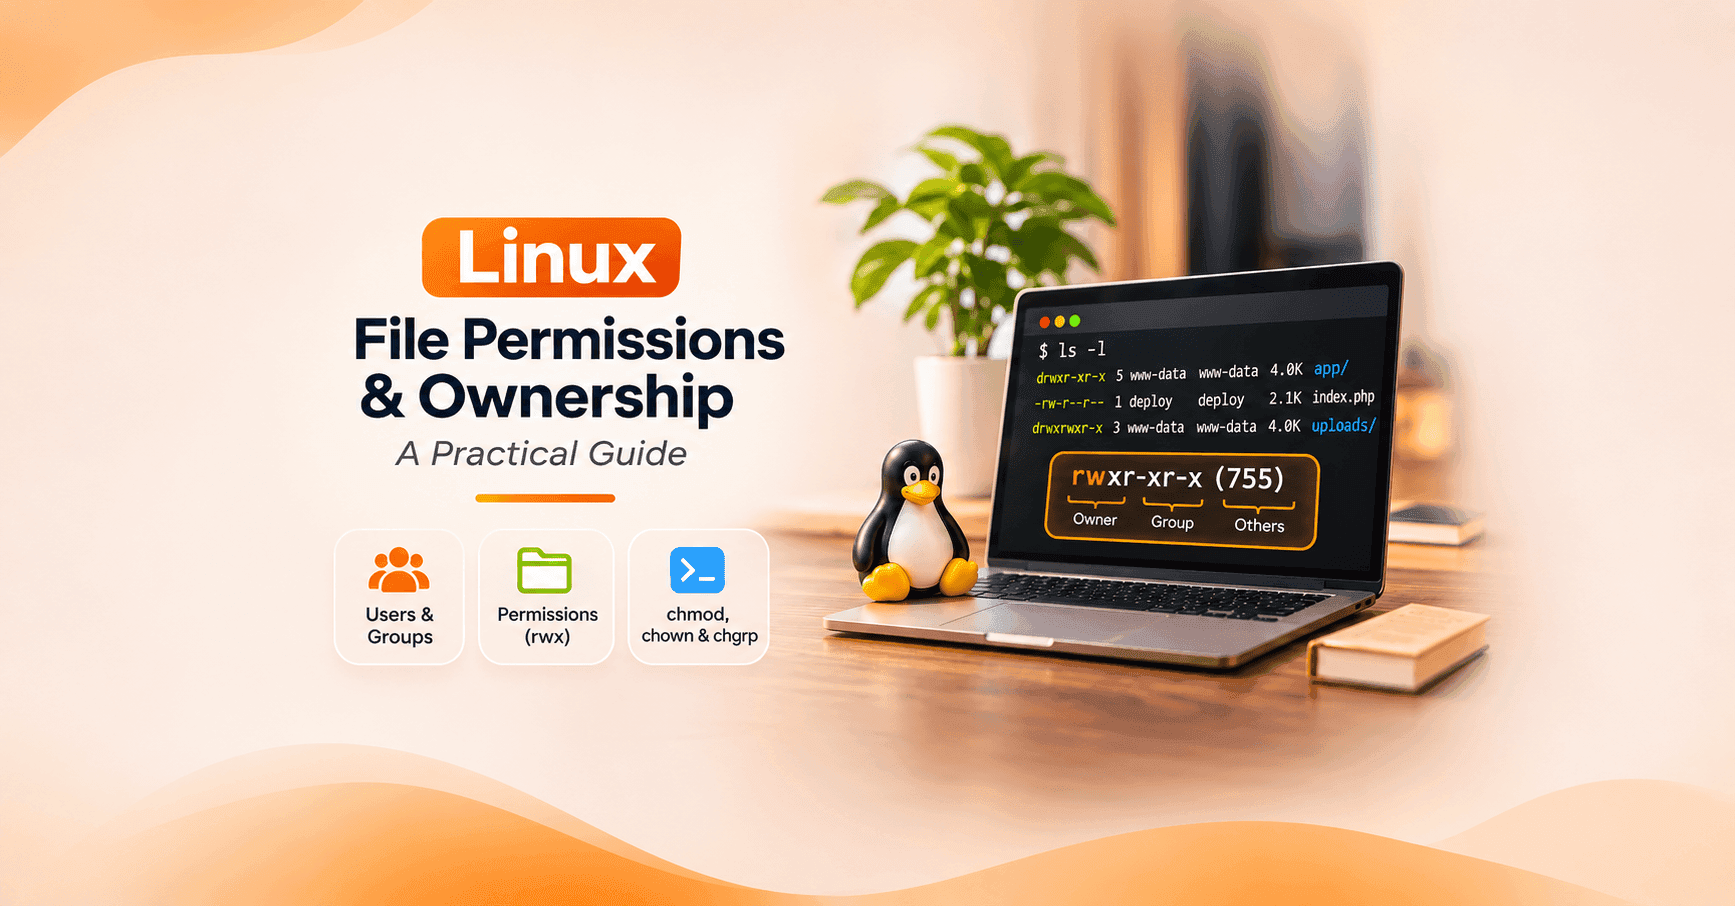
Learn Linux file and directory permissions, users, groups, chmod, chown, umask, ACLs, and security best practices with practical examples.
Introduction A critical vulnerability in the Linux kernel's TCP networking subsystem has raised security concerns for organizations running Linux-based servers, cloud infrastructure, and containerized workloads. Tracked as CVE-2026-98432, the vulnerability has received a CVSS 3.1 score of 9.8 out of 10 from the Linux kernel CVE authority. The flaw involves a race condition that can cause the kernel to access memory after it has already been released, potentially resulting in system crashes o
Introduction A server can have a fully patched operating system, properly configured firewall rules, endpoint monitoring, and Secure Boot enabled—and still be vulnerable before any of those protections have an opportunity to work. That is the concern raised by CVE-2026-97631, a critical vulnerability discovered in the UEFI firmware code used to initialize and boot many modern servers. Disclosed by the TianoCore project on October 22, 2026, the vulnerability carries a CVSS 4.0 severity scor